I sit on your side of the evaluation table. From requirements gathering through demos, proofs of concept, and solution architecture, my job is to show — not just tell — how application security tooling fits the way your teams actually ship code.
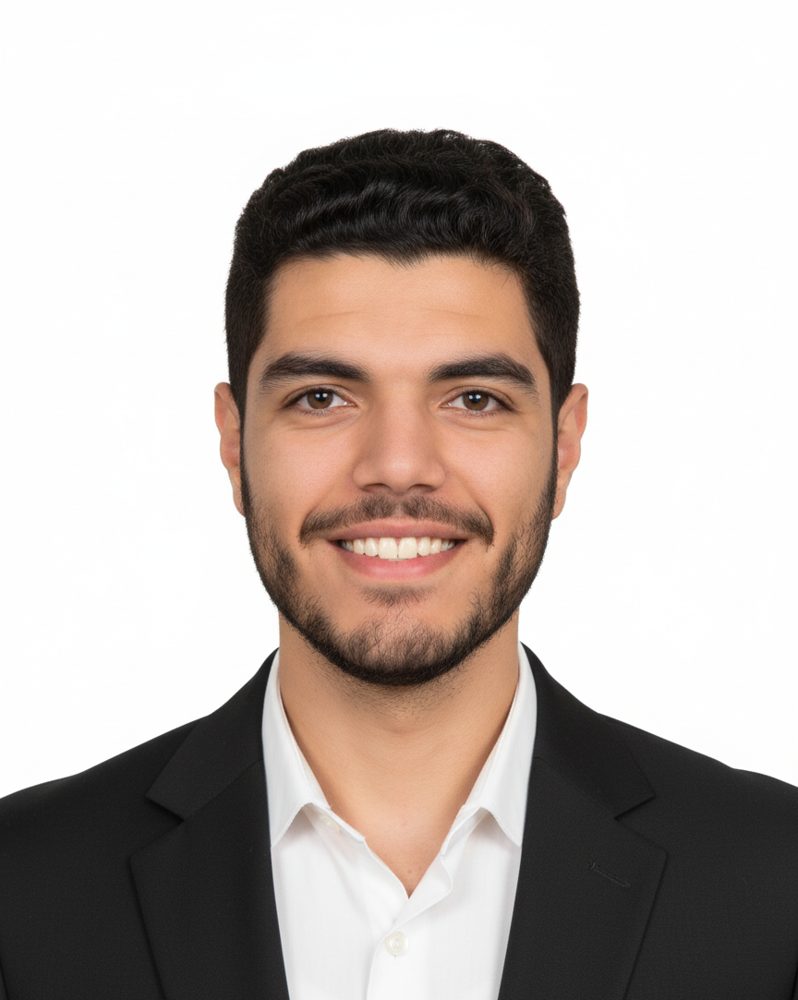
Background, and how I approach the presales side of security.
02What I actually do for you — from architecture to implementation.
03Where this comes from — Prosoft, and offensive security before that.
04CTF solutions, vulnerability research, and AppSec challenge breakdowns.
05Ways to reach me, and what to send if you're evaluating tooling.
12 published writeups across 4 topics — CTF solutions, code review challenges, and vulnerability research from real targets.
This is a working shell, not a screenshot. Ask about my background, search the writeups by keyword, or just poke around — every answer is served from the site itself, with no backend and nothing to sign up for.
↑ ↓ history · Tab complete · Ctrl+L clear